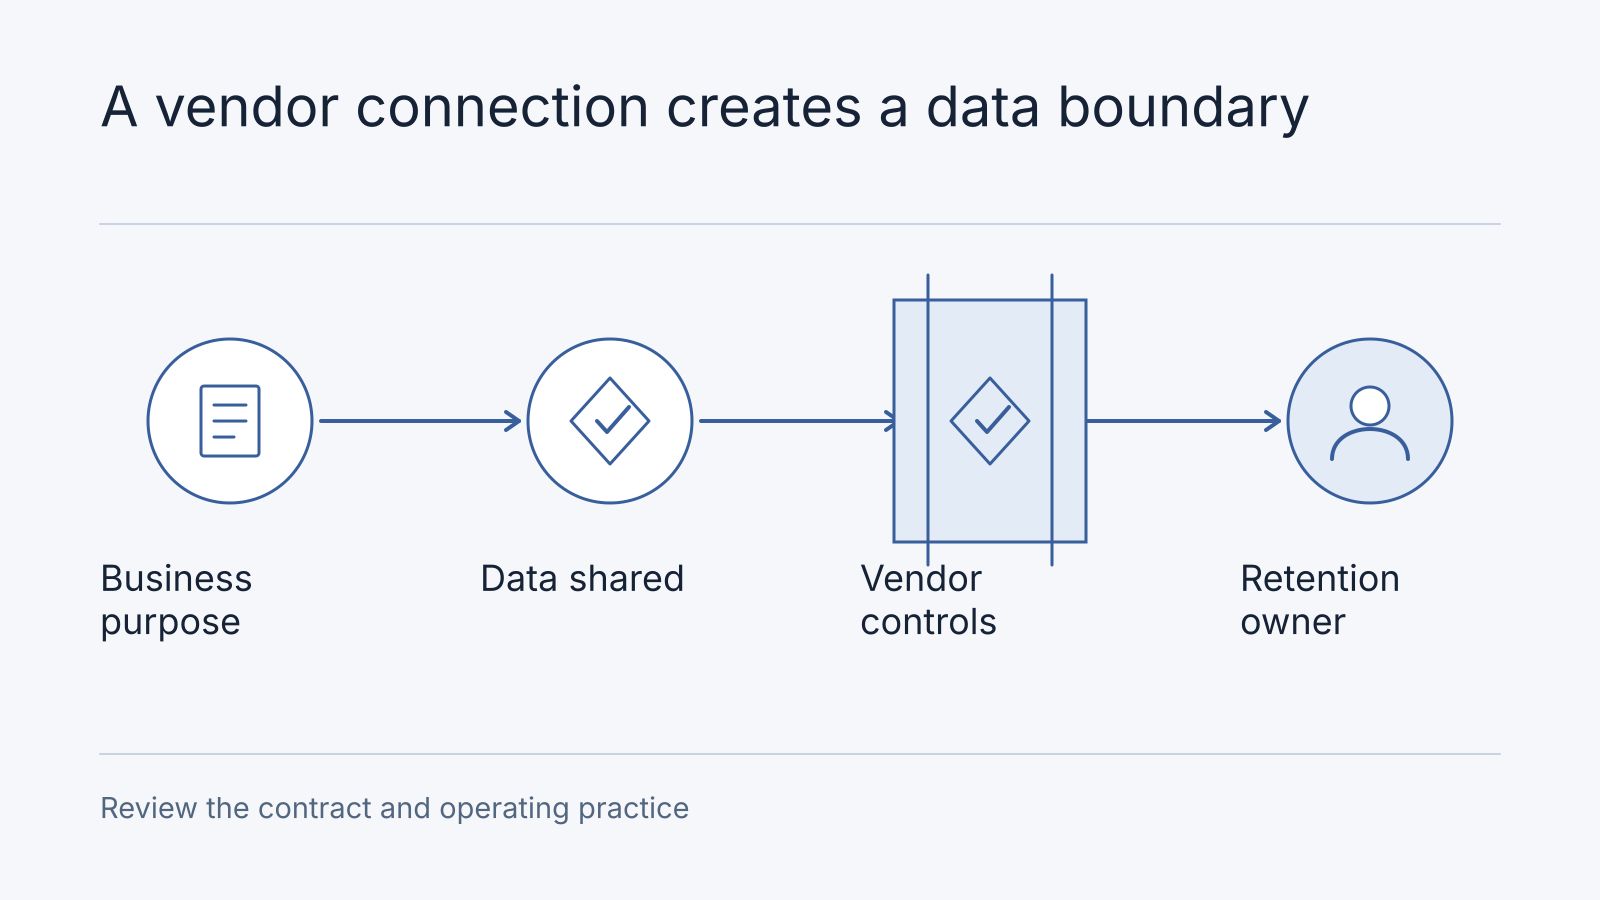
A vendor review should follow the personal data: who receives it, why they process it, where they store it and what happens when access or the contract ends. A cloud region or supplier’s registered address cannot answer all of those questions.
This guide, reviewed on 13 September 2026, explains how to scope a Malaysian software supplier assessment. Read it alongside our website PDPA guide.
Classify the actual processing role
A controller determines the purposes of processing; a processor acts on a controller’s behalf. Classify each activity rather than assigning one label to every supplier. A payment provider may act as a controller for its own regulatory purposes. An agency that builds a site without processing personal data is not automatically a processor merely because it supplied code.
The 2024 amendment gives processors direct Security Principle duties. Controller notification to the Commissioner under section 12B is distinct from a processor escalating an incident to its customer. Contracts should make that escalation prompt and practical. Act A1727.
Do not assume every vendor must appoint a DPO. Apply JPDP’s thresholds for data volumes or regular and systematic monitoring, and identify the appropriate contact for suppliers outside those criteria. JPDP FAQ.
Assess cross-border transfers under section 129
Malaysia’s amended transfer framework allows transfers where the destination has substantially similar law or adequate protection, alongside the grounds in section 129(3). Document the basis and supporting assessment. Contractual safeguards can contribute to that analysis; signing generic clauses does not create an automatic approval. The PDPA does not generally require all personal data to remain in Malaysia. JPDP cross-border transfer guideline.
A cloud-region setting is only one part of the inventory. Check support access, backups, disaster recovery, logs, analytics, email and subprocessors. If the supplier cannot establish where a relevant activity occurs, record the uncertainty before approving the flow.
Avoid claiming that the PDPA applies to every offshore supplier solely because the data concerns Malaysian individuals. Territorial scope requires an assessment under sections 2 and 3. Equally, offshore location does not automatically mean no contractual recourse. Official Act 709.
Put the operating responsibilities in the contract
These are recommended procurement safeguards. They are not presented as a verbatim list of clauses universally required by Malaysian law.
| Topic | What to agree |
|---|---|
| Processing scope | Data categories, purposes and permitted instructions |
| Security | Relevant technical controls and responsibility for operating them |
| Subprocessors | Which parties are used and how changes are communicated |
| Location | Storage, access and recovery locations, plus transfer safeguards |
| Incidents | Escalation contacts, information required and contractual response expectations |
| Requests | Assistance with access, correction, retention and portability workflows |
| Exit | Return, deletion, backup expiry and evidence of completion |
| Assurance | Available audit evidence, review rights and remediation responsibilities |
Choose escalation deadlines that leave the controller time to assess and meet applicable notification requirements. An incident runbook should identify who decides whether notification is required and who submits it; it should not rely on a developer being available to interpret the law during an outage.
Verify integrations rather than relying on labels
For analytics, distinguish consent collection from technical enforcement. Advanced Google consent mode can send cookieless pings before consent. Server-side tagging also does not itself block transmission. Review the exact deployment and data flow. Google consent mode documentation.
For payments, distinguish privacy roles, financial authorisations and card-security requirements. For hosting, investigate whether the supplier’s actual service falls within Malaysian cloud licensing rules. For development access, use named accounts, limited privileges and revocation at exit.
Self-hosted tools can still call remote model APIs or SaaS endpoints. Local ownership and Malaysian invoicing do not replace the transfer assessment.
Follow one support message across providers
In an illustrative vendor inventory, a support message enters the website host, is stored in a helpdesk and is sent through an email provider. If an AI service drafts a reply, record the material sent to that endpoint too. For each destination identify the contracting entity, processing purpose, locations, subprocessors, retention/deletion behaviour, account owner and evidence date. Mark unknown roles or locations unverified; do not infer them from a brand’s headquarters.
An exit rehearsal exports permitted open tickets, confirms readable attachments and preserves references needed for the new system. Then document deletion requests and the provider’s treatment of backups, logs and contractual retention. Removing a user account is not evidence that every retained copy has been deleted. The privacy owner reviews the actual obligations and commitments.
Frequently Asked Questions
What if a supplier will not disclose a required detail?
Record the missing evidence, ask for an appropriate contractual or assurance response and let the responsible business/privacy owner decide whether the residual uncertainty is acceptable. Do not fill the field with an assumption.
Can a developer approve a cross-border arrangement for us?
The developer can map technical data flows and configure agreed controls. Legal applicability and the organisation’s approval belong with the responsible reviewers. Bring the inventory to the preparation guide before an integration scope is committed.
For each supplier, make a short inventory: what personal data it receives, why it receives it, which party decides the purpose, where it is processed, who can access it and how an incident reaches the responsible owner. Use that evidence to assess roles and transfer arrangements with legal advice. A contract template or Malaysia-based address alone cannot establish the correct role or make an overseas transfer lawful.
Can we use a cloud region outside Malaysia?
Potentially. Document the relevant section 129 basis and assess other applicable sector or contractual restrictions before selecting the region.
Is a DPA enough to approve a supplier?
It is part of the evidence. Check the supplier’s actual controls and data flows, and make sure operational responsibilities are understood.
Does hiring a Malaysian agency remove controller liability?
No. A local counterparty may simplify coordination or enforcement, but statutory responsibilities and the actual processing arrangement still matter.
Use our architecture audit service to scope a vendor inventory, identify missing evidence and prioritise technical changes.